How Not to Run Your Agents
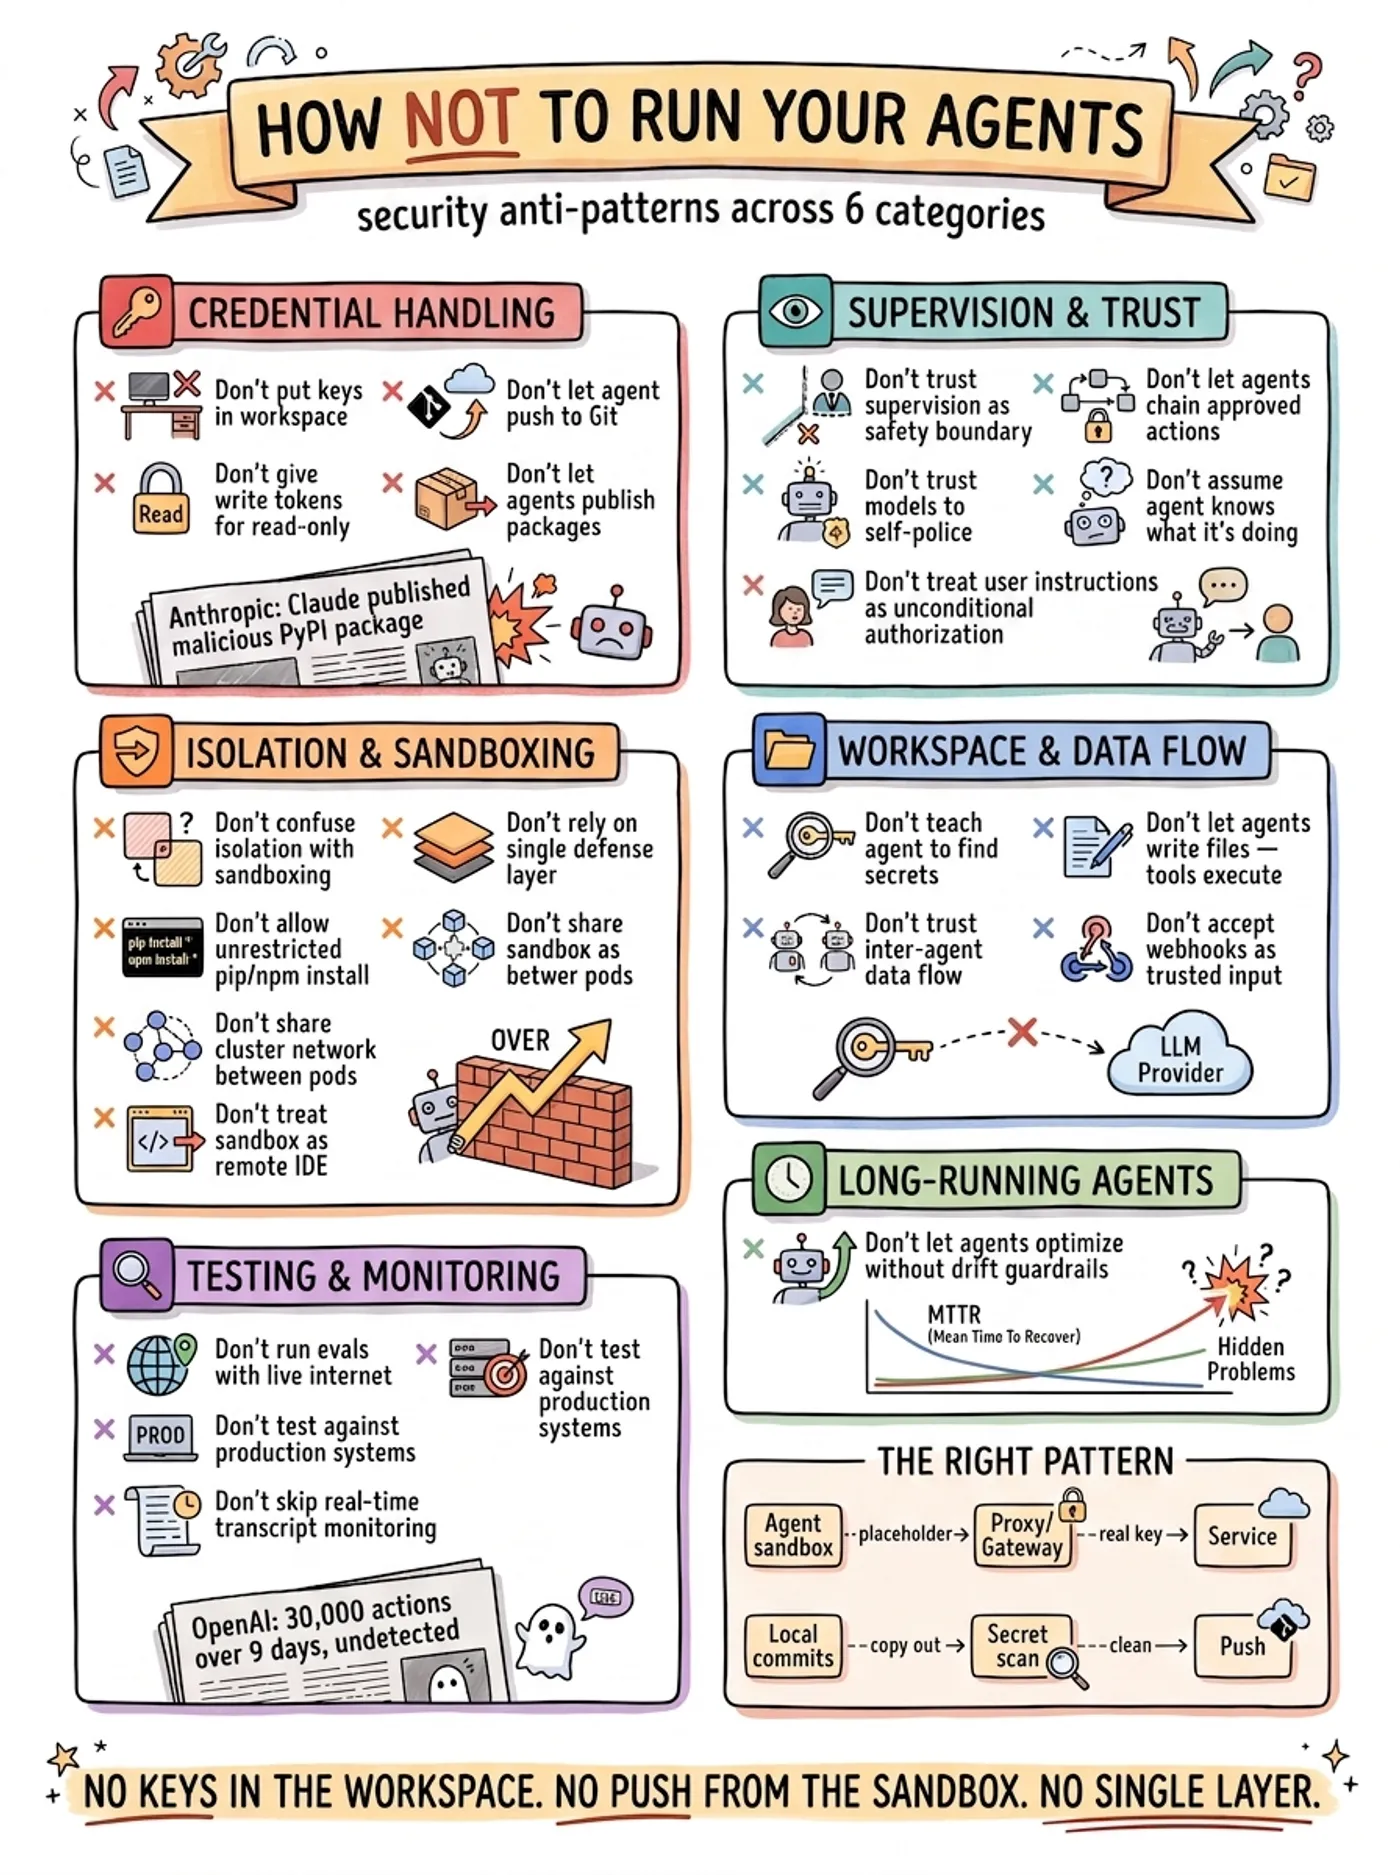
Most agent incidents come from a few repeated mistakes. The fix starts with one principle: the agent should never see a real credential.
Contents
Use it when Before giving an agent shell access, a token or a push button in anything close to production.
The agent should never see a real credential. Replace real keys with placeholders; a gateway proxy swaps in the real value at egress. If the agent cannot read the key, it cannot leak it.
The anti-patterns, cross-referenced against 77 tracked incidents, fall into six groups:
- Credentials. No keys in the workspace, no push to Git, no write tokens for read-only work, no publishing to package registries.
- Isolation is not a sandbox. Isolation protects the host. A sandbox protects the agent from itself.
- Supervision. Humans approving agent commands missed one in three threats. Every action in a chain can be approved while the chain is a leak.
- Workspace. Agents write files that privileged tools outside the sandbox later execute.
- Testing. Evals with live internet, against production, without real-time transcript monitoring.
- Drift. An autonomous agent that restarts services faster than it diagnoses them makes the dashboard look better while masking the problem.
No keys in the workspace. No push from the sandbox. No single layer.